Feds Seize & Disrupt Major Gootloader Malware Botnet
Original headline: Gootloader Malware Disrupted After Infecting 25,000 Computers — securityaffairs.com
More in Cybersecurity news
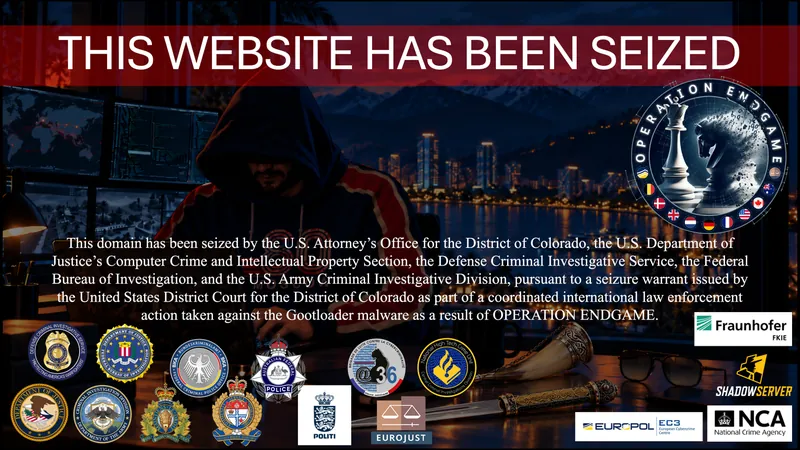
An international coalition of law enforcement agencies, led by the U.S. Department of Justice, has successfully disrupted the Gootloader malware operation. The coordinated action involved taking down over 100 infected servers, seizing U.S. domain names used to control the botnet, and notifying victims worldwide. Since 2018, Gootloader had infected approximately 25,000 computers, spreading primarily through compromised WordPress sites.
The malware operated as a sophisticated 'access-as-a-service' platform, where its operators sold access to infected machines to ransomware gangs like REvil and SunCrypt. This led to at least 44 documented ransomware attacks against U.S. targets, causing an estimated $28.8 million in losses, including within the Defense Industrial Base. This takedown, conducted under the broader Operation Endgame initiative, represents a significant blow to the criminal malware-for-hire ecosystem.
Read the original at securityaffairs.com
Satirical commentary on real tech news, summarised with AI. Read the original source for the facts. How ZeroDaily works